What are you looking for?
SBOM Manager
Transform binaries into SBOMs. Manage any SBOM. Secure the product supply chain.
Our Offerings
SBOM Generator
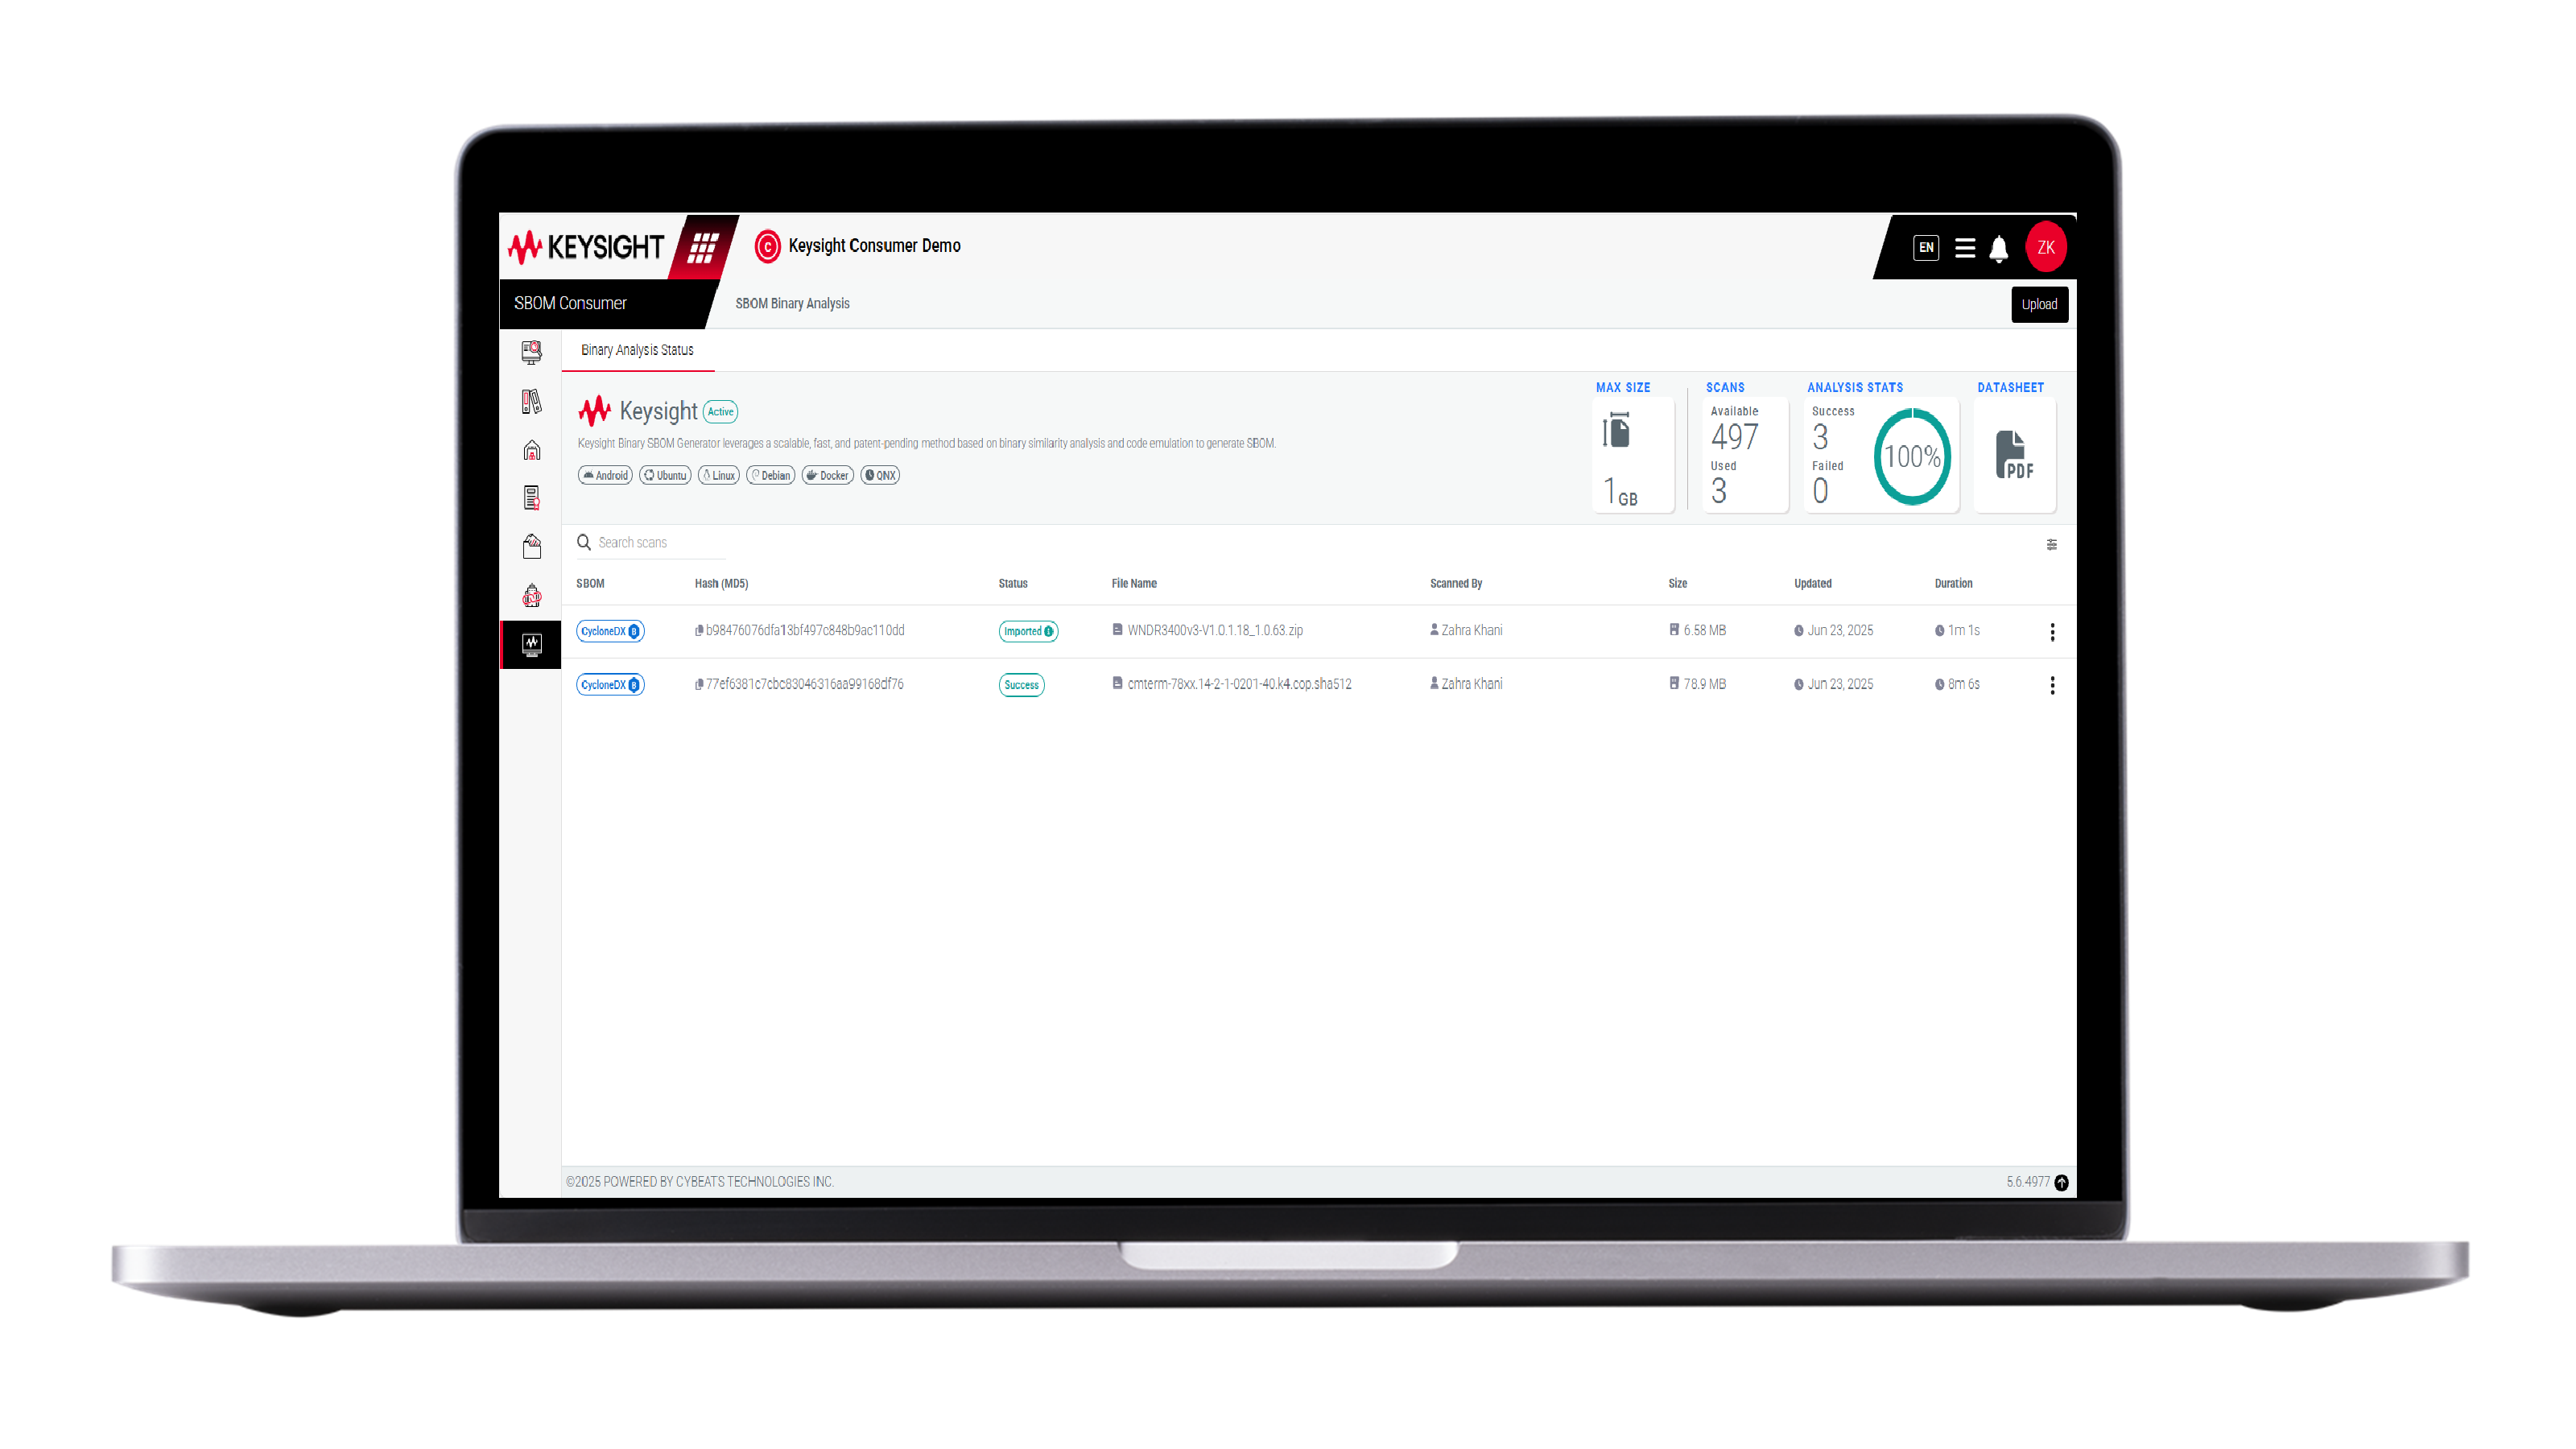
The Keysight Software Bill of Materials (SBOM) Generator is a next-generation binary analysis engine designed to extract highly accurate SBOMs from compiled binaries, firmware, and containers. It uses patent-pending binary similarity analysis and code emulation techniques to detect both open-source and proprietary components, without requiring source code or build access.


SBOM Studio
SBOM Studio is the central hub for managing and operationalizing SBOMs. It enables full-lifecycle SBOM governance, from validation and enrichment to continuous vulnerability monitoring and regulatory compliance. Whether your SBOMs come from Keysight SBOM generator or third parties, SBOM Studio ingests, scores, enriches and monitors them.

SBOM Consumer
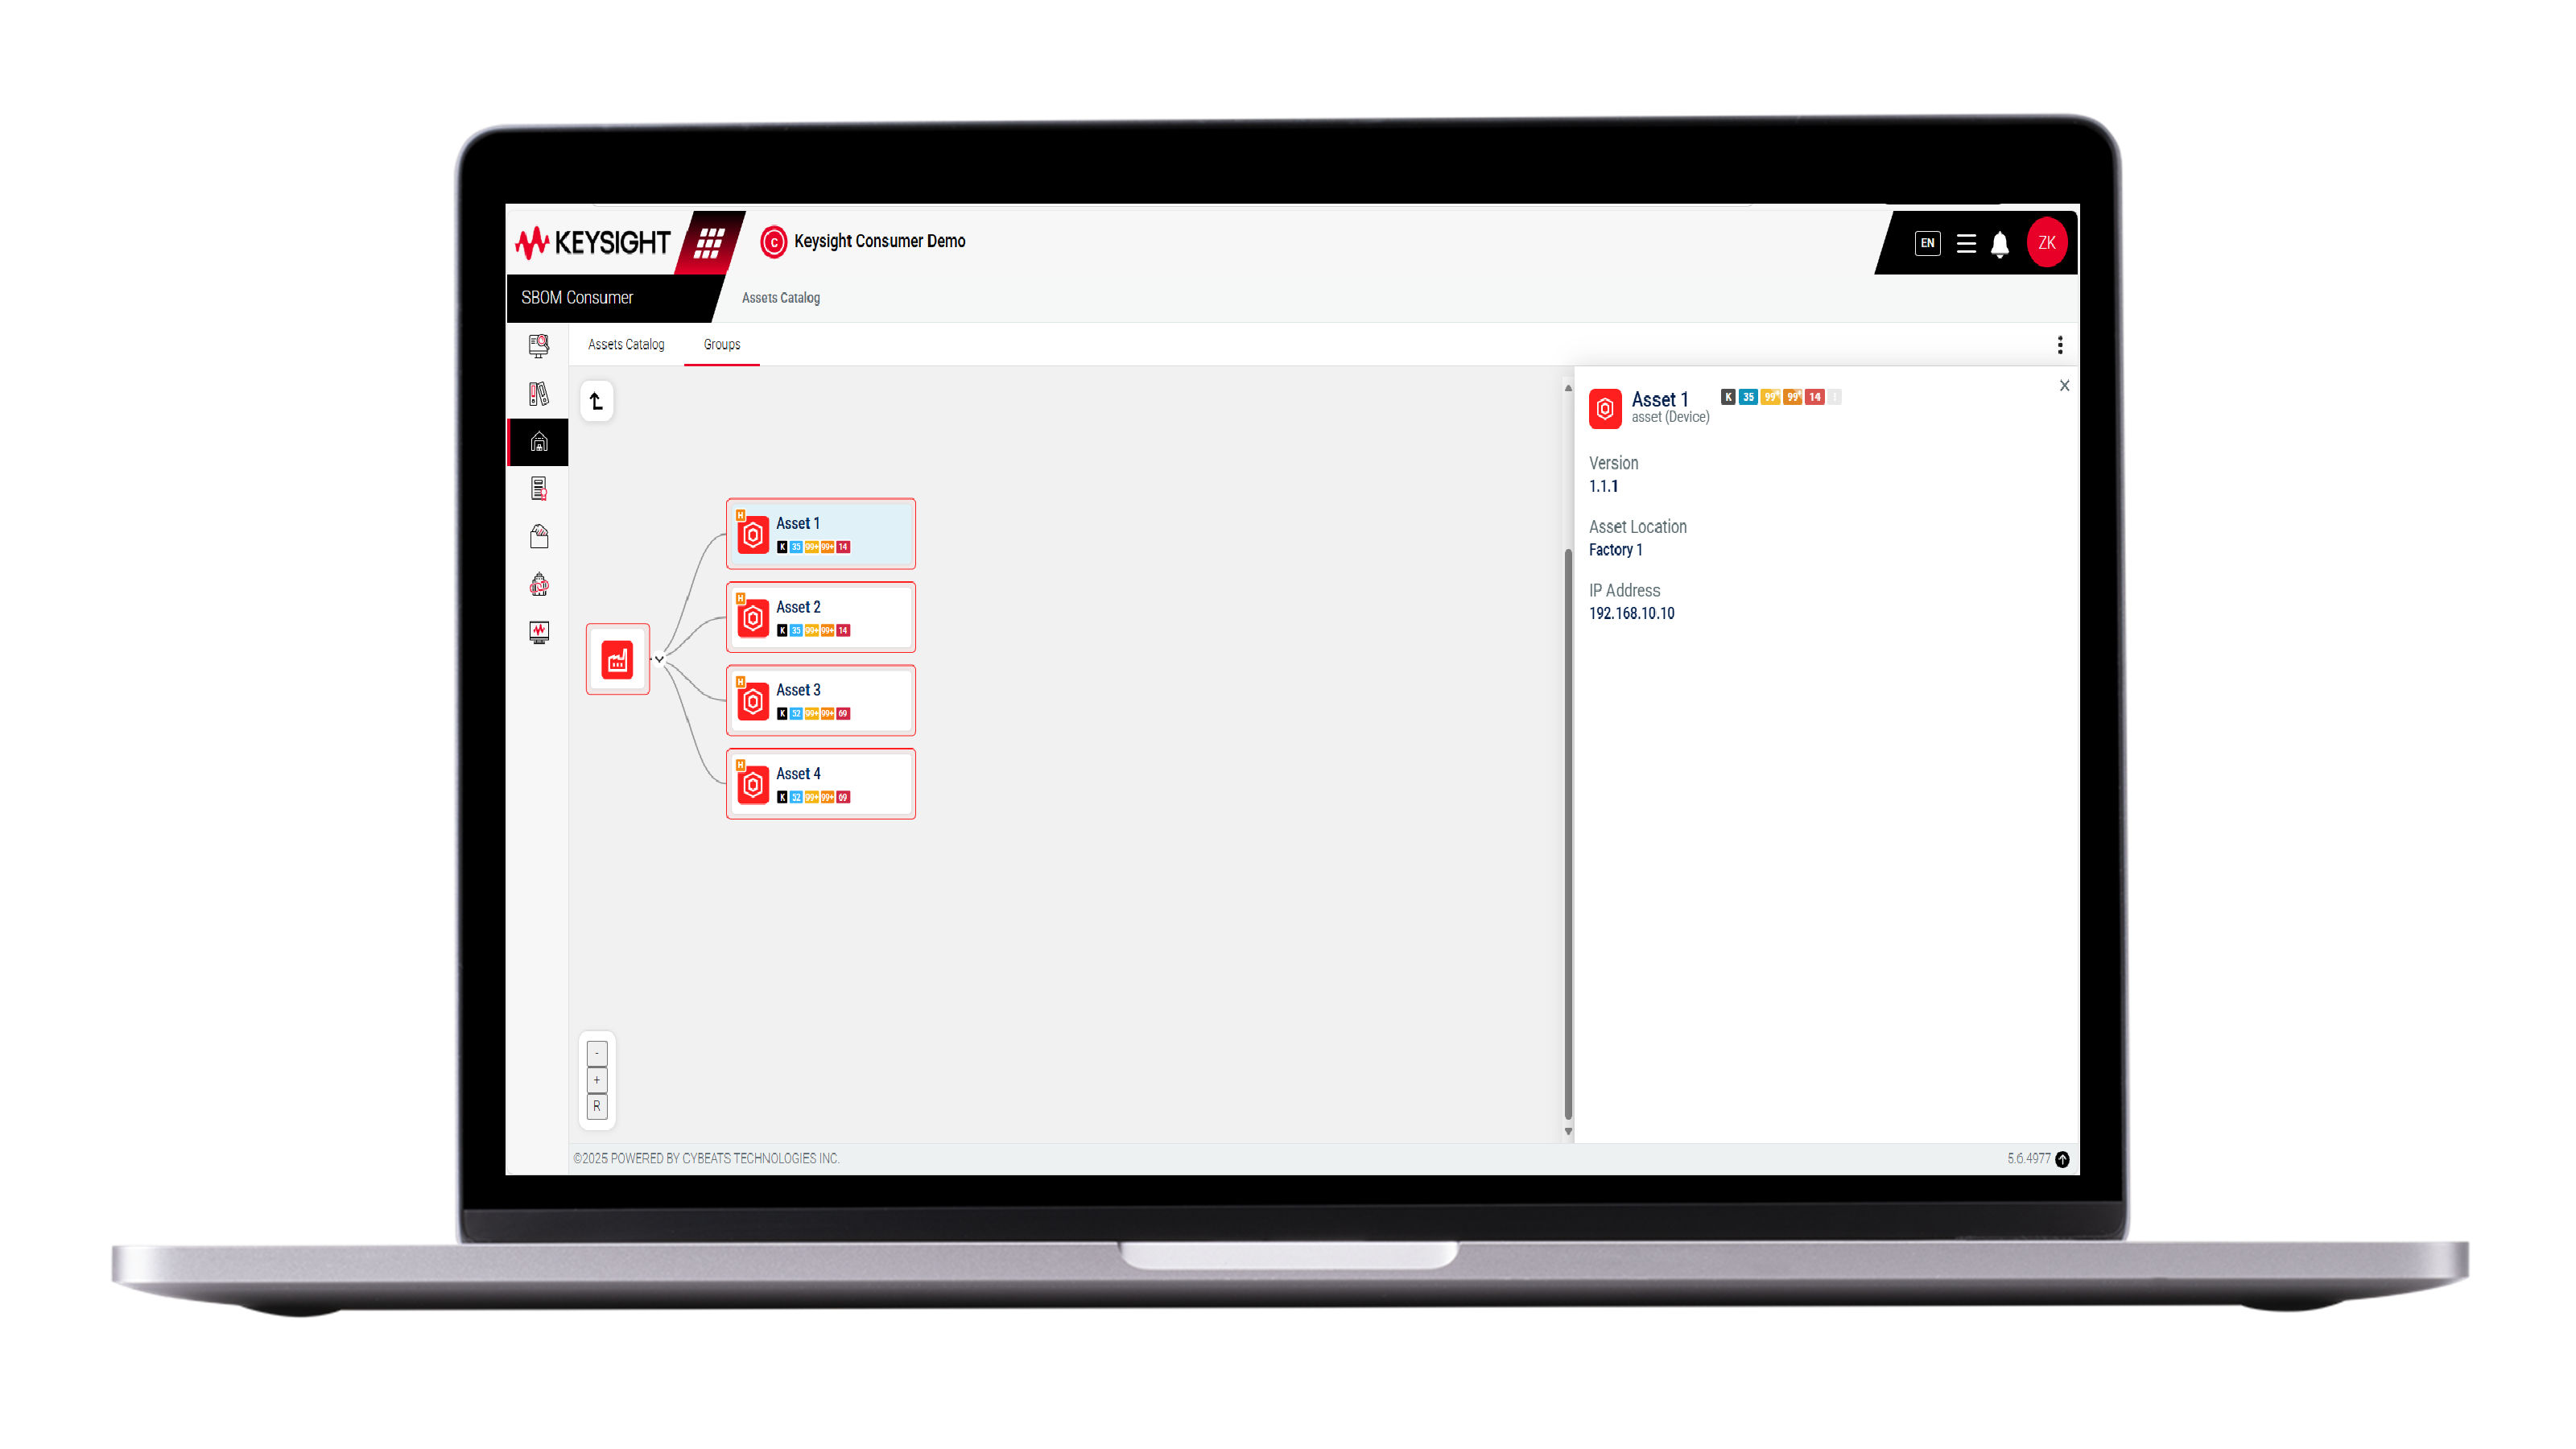
SBOM Consumer enables software and device buyers to validate and monitor SBOMs received from suppliers and vendors. It provides real-time threat visibility, SBOM structure validation, and ongoing vulnerability tracking, empowering buyers to trust the products they acquire and deploy.
Highlights
SBOM Generator
- Binary-Only Analysis
- Accurate SBOM Generation
- High Component Coverage
- OSS and Closed-Source Detection
- First-Party Identification
- CycloneDX and SPDX Output
SBOM Studio
- SBOM Inventory and Management
- Vulnerability Lifecycle Management
- VEX and VDP
- Regulatory Compliance
- EU CRA and FDA
- Licensing Risk Assessment
- SBOM Sharing and Exchange
SBOM Consumer
- Automated SBOM Ingestion
- SBOM Validation
- Comprehensive Cataloging
- Integration with Asset Managements
- Continuous Vulnerability Monitoring
- Contextualized Threat Intelligence
- Real-Time Alerting
- Regulatory Compliance
Proven across Industries: SBOM Studio in Action
Telecom OEMs producing network equipment like base stations, routers, and CPEs deal with embedded software that often integrates a wide array of open-source, proprietary, and third-party components. They use the Keysight SBOM Generator to analyze firmware images and extract accurate SBOMs directly from binaries, ensuring visibility into all software components, including those inherited from upstream suppliers.
These SBOMs are then managed within SBOM Studio, enabling product security and compliance teams to enrich them with vulnerability and threat intelligence data, track usage of high-risk components, enforce policy (for example, banning outdated libraries), and respond to regulatory demands like the EU Cyber Resilience Act or NTIA SBOM mandates.

SBOM Studio also supports secure SBOM sharing with customers and partners, enabling transparent collaboration, faster vulnerability coordination, and streamlined compliance reporting across the telecom supply chain.
Vendors of industrial automation products, including PLCs, RTUs, gateways, and control systems, often integrate legacy software and third-party code that lacks modern software transparency.
Using the Keysight SBOM Generator, these vendors can analyze the firmware they ship and generate binary SBOMs to gain visibility into their embedded software stack. With SBOM Studio, these SBOMs are centrally managed, versioned, and enriched with vulnerabilities and threat intelligence data.


Product and engineering teams can track software reuse across models, document compliance with IEC 62443 secure development practices, and deliver detailed SBOMs to industrial customers, improving transparency and trust while enabling a more mature product security lifecycle.
Medical device vendors are increasingly expected to provide full SBOMs during FDA premarket submission and maintain software transparency throughout the device lifecycle. The Keysight SBOM Generator enables these manufacturers to generate SBOMs directly from binary firmware, even when parts of the codebase come from legacy or third-party vendors.
SBOM Studio allows them to manage these SBOMs, track CVEs across releases, link vulnerabilities to specific models or UDI numbers, and generate exportable reports for regulators and customers.


SBOM Studio also supports incident response during coordinated disclosure events and postmarket surveillance by allowing teams to rapidly assess impact across products and firmware versions, coordinate mitigations, and support downstream patching or customer notifications.
Vendors of IP cameras, smart appliances, printers, and home networking devices need scalable ways to manage software risk across diverse product lines. The Keysight SBOM Generator gives them the ability to analyze firmware at scale, revealing undocumented or vulnerable components.
With SBOM Studio, security teams can organize SBOMs by model and firmware version, apply component policies, and detect reuse of deprecated or banned libraries. It supports internal secure development frameworks (for example, NIST SSDF), enables faster response to public CVEs, and allows better coordination between engineering, product, and compliance teams.

SBOM Studio also supports the generation of Vulnerability Exploitability eXchange (VEX) statements, helping vendors communicate whether vulnerabilities are exploitable in the context of their products. Together, these capabilities help ensure devices ship with well-documented and traceable software stacks in line with emerging regulations such as the EU Cyber Resilience Act (CRA).
Software-defined vehicles rely on dozens of ECUs, each running distinct firmware built from a complex mix of in-house, open-source, and third-party software. The Keysight SBOM Generator enables OEMs and Tier-1 suppliers to extract accurate SBOMs directly from binary firmware, allowing them to verify that received components match expectations, contain no undocumented software, and meet internal security baselines.
These SBOMs are then managed in SBOM Studio, where cybersecurity and engineering teams can centrally track third-party software usage across vehicle models and ECU generations, monitor license obligations, and enforce internal policies. SBOM Studio provides built-in vulnerability management, automatically correlating vulnerabilities to specific components, enabling rapid triage and remediation workflows. It also supports the creation of Vulnerability Exploitability eXchange (VEX) statements to help teams communicate whether identified vulnerabilities are exploitable in the actual product context, a critical capability for regulatory reporting and customer assurance.


Secure SBOM sharing features make it possible to collaborate with suppliers, compliance bodies, and partners while maintaining control over what information is disclosed. Together, these capabilities help automotive organizations comply with cybersecurity regulations such as UNECE WP.29 R155 and ISO/SAE 21434, while reducing risk across the software supply chain and supporting a continuous software assurance strategy throughout the vehicle lifecycle.
Proven across Industries: SBOM Consumer in Action
Operators managing telecom infrastructure often face the challenge of receiving hardware from multiple vendors with inconsistent or missing SBOMs. With the Keysight SBOM Generator, they can independently extract SBOMs from firmware updates or received binaries, verifying the accuracy and completeness of supplier-provided SBOMs, or generating them from scratch if needed.
These verified SBOMs are then fed into SBOM Consumer, which enables security operations teams to receive real-time CVE alerts, assess impact across their installed asset base, and prioritize patching or mitigation activities.

This is critical for maintaining network uptime, defending against software supply chain attacks like RegreSSHion, and maintaining compliance with national security regulations.
Asset owners in sectors like energy, utilities, and manufacturing often run legacy OT systems with opaque software stacks. Even when vendors supply SBOMs, these are frequently incomplete or outdated.
With the Keysight SBOM Generator, operators can extract SBOMs from device firmware, verifying vendor claims and gaining independent visibility into vulnerable software components. SBOM Consumer enables ongoing monitoring of security advisories, automatic CVE correlation, and vulnerability monitoring across thousands of fielded assets.

It can integrate with existing asset management tools, enabling operators to gain detailed visibility into their product supply chain risks, prioritize mitigations, plan upgrades, and support compliance with NIS2 and critical infrastructure protection regulations.
Government bodies, whether civilian, defense, or critical national infrastructure operators, are under growing pressure to secure the software supply chain across everything from office printers and networking equipment to field-deployed communications systems and tactical embedded devices. These organizations often receive products with limited software transparency.
The Keysight SBOM Generator empowers them to independently analyze firmware or software binaries received from contractors and suppliers, verifying the accuracy and completeness of SBOMs or generating them when absent. This ensures they are not blindly trusting vendor declarations and have a verifiable record of software contents. After SBOMs are generated, SBOM Consumer enables these agencies to correlate software components against evolving threat intelligence feeds, prioritize vulnerabilities based on mission impact, and support compliance with national cybersecurity directives (such as Executive Order 14028, OMB M-22-18, and CISA KEV tracking).

For agencies that also act as solution integrators or develop internal platforms, SBOM Studio provides central SBOM management, tracking component usage across internally developed software, and ensuring full lifecycle security management. The combined platform gives governments a scalable way to verify, monitor, and secure the software they depend on, even in high-assurance or classified environments.
Hospitals often deploy critical connected devices, such as infusion pumps, diagnostic equipment, and patient monitors, without clear visibility into their underlying software components.
With the Keysight SBOM Generator, IT and clinical engineering teams can analyze firmware and extract SBOMs for in-use devices, verifying or supplementing what vendors may have provided. These SBOMs feed into SBOM Consumer, which enables proactive vulnerability monitoring, alerts on high-severity CVEs, and integration with patch management and procurement workflows.


This supports FDA postmarket expectations, reduces operational risk from insecure devices, and empowers hospitals to make informed security decisions when acquiring or maintaining clinical systems.
Organizations deploying a wide variety of products, from smart door locks and surveillance systems to network appliances and embedded VoIP phones, rarely receive complete SBOMs from vendors.
With the Keysight SBOM Generator, they can independently extract SBOMs from firmware or container, or verify SBOMs provided by vendors, ensuring accurate visibility into their products. These SBOMs are used by SBOM Consumer to continuously monitor for vulnerabilities, correlate them to affected products, and integrate with asset inventories.

This proactive posture helps protect enterprise networks from supply chain risks and aligns with frameworks like ISO 27402 and NIST CSF 2.0.
Extend the Capabilities
Featured Resources


Want help or have questions?